Pioneering -
Innovative -
Creative


QTSC9, Quang Trung Software City, Trung My Tay Ward, Ho Chi Minh City, Vietnam


OWASP Top-Ten: High-Priority Security Risks Every Developer Should Know
Understanding and implementing OWASP Top-Ten helps you address common security vulnerabilities. By applying these security measures, you ensure better protection for your web application against attacks and threats.
Understanding and mitigating fundamental security risks is crucial whether you're building or managing a web application. Security threats to web applications aren't just challenges; they pose serious dangers to user data and information safety. OWASP Top-Ten provides an in-depth view of critical risks that developers and system administrators must recognize and rectify. Let's delve into the details to comprehend each risk and how to prevent them.
Injection
Injection isn't solely a method for attackers to introduce malicious code into your system; it also exploits vulnerabilities in data processing. For instance, SQL injection often occurs when users input strings containing SQL code into search or login fields. This could lead to retrieving user information or even controlling the database.
Prevention Measures:
- Use parameterized queries and prepared statements.
- Thoroughly validate and filter user-inputted data.
- Implement strict data access control mechanisms.
Broken Authentication
When authentication security is compromised, attackers can attempt password guessing, hijack logins, or even expose user personal information.
Example and Prevention:
- Enforce strong passwords and configure limited incorrect login attempts.
- Employ password hashing with robust algorithms like bcrypt or sha-256.
Sensitive Data Exposure
Improperly safeguarded sensitive data can easily be exposed and become a target for attackers.
Remediation:
- Encrypt sensitive data during storage and transmission.
- Use HTTPS protocol for data transmission.
XML External Entities (XXE)
XXE allows attackers to inject malicious XML entities into XML input data, leading to severe consequences like sensitive data retrieval or remote attacks.
Example:
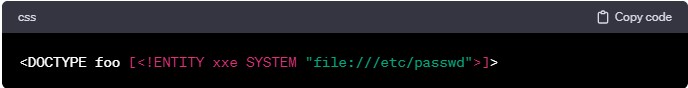
Preventive Measures:
- Disable external entity XML processing or use safer XML processing libraries.
- Inspect and remove unsafe entity declarations from XML input data.
Broken Access Control
This vulnerability enables attackers to access resources or functions they aren't authorized to access.
Example: Users without permission accessing admin pages due to a lack of permission checks.
Prevention Strategies:
- Verify and confirm access rights at the user and role levels.
- Implement strict permission checks and rigorous validation in source code.
Security Misconfiguration
This flaw often occurs when system configurations aren't properly implemented, leaving hidden security vulnerabilities.
Example: Default settings for demo accounts or easily accessible default admin directories.
Preventive Measures:
- Review and eliminate unnecessary demo accounts and sample data.
- Accurately configure security settings while ensuring regular updates.
Cross-Site Scripting (XSS)
XSS is a vulnerability that allows attackers to inject malicious JavaScript into a website to execute on the user's browser.
Example:
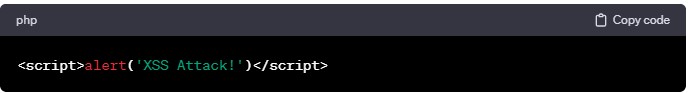
Preventive Measures:
- Use output encoding libraries or escape mechanisms to prevent XSS.
- Thoroughly validate and inspect user-inputted data before displaying it on the website.
Insecure Deserialization
This vulnerability arises when deserializing objects lacks strict control, allowing attackers to inject and execute malicious code.
Example: When deserializing JSON, attackers can inject additional malicious data fields.
Preventive Actions:
- Only deserialize objects from trusted sources.
- Validate and clean data before deserialization.
Using Components with Known Vulnerabilities
This risk occurs when using components with known security vulnerabilities that haven't been patched.
Example: Using an outdated version of a framework with disclosed security flaws.
Preventive Actions:
- Ensure frequent updates for components and frameworks to apply the latest patches.
- Use version control tools to manage and update components.
Insufficient Logging & Monitoring
This risk involves a lack of proper logging measures and monitoring application activities.
Example: Inadequate logging of access or lack of alerts for abnormal activities.
Preventive Measures:
- Maintain comprehensive logs of access, errors, and significant events.
- Set up alerts and notifications for suspicious activities.
OWASP Top-Ten provides an overview of top security risks in web applications and the necessary remediation steps. Ensure that implementing these security solutions will help safeguard your application against potential threats.
related post

Explore Moodle LMS E-learning, its features, benefits, limitations, and use cases. Learn when a custom LMS solution from Aegona may better fit your needs.

84% of developers use AI, yet only 5.4% of firms fully trust its output. Discover how software companies divide work between humans and AI, and optimize costs with IT Staff Augmentation

Wix is a user-friendly website builder that helps you create, customize, and manage professional websites without coding using drag-and-drop tools and ready-made templates.

Learn how to integrate Google Pay, Apple Pay, and payment gateways into your website. Explore payment API integration, security, and online payment solutions with Aegona.

Discover Odoo Manufacturing for automotive, electronics, food, furniture, and textile industries. Aegona customizes Odoo to fit your production workflows.


Discover TourFlow, tour management software for travel agencies to organize customer data, manage tour products and departures, and track bookings.

OpenAI Ads brings a new advertising opportunity to ChatGPT. Explore how ChatGPT Ads work and what businesses should know about advertising in the AI era.

Shopify website design and development tailored to your business, with custom themes, integrations, features, and maintenance.

AEO vs OpenAI Ads: discover the difference between AI Search optimization and ChatGPT advertising, and what businesses should consider in the AI era.


Custom PoC/MVP development services by Aegona to validate software ideas, reduce development risks, and build scalable solutions for your business.

Explore Aegona’s MCP Server Development Services to connect AI and AI Agents with ERP, CRM, databases, APIs, and enterprise systems for smarter automation.

Scale your development team with Aegona’s Staff Augmentation Services. Hire skilled Java, PHP, Fullstack Developers in Vietnam for your projects.

